Compliance without the document chase.
Typical compliance tools make you upload screenshots and documents for every control. Shield already knows your computers, accounts and backups - so it collects the evidence itself, fixes what fails with one click, and writes your policies from your real settings.
See it working
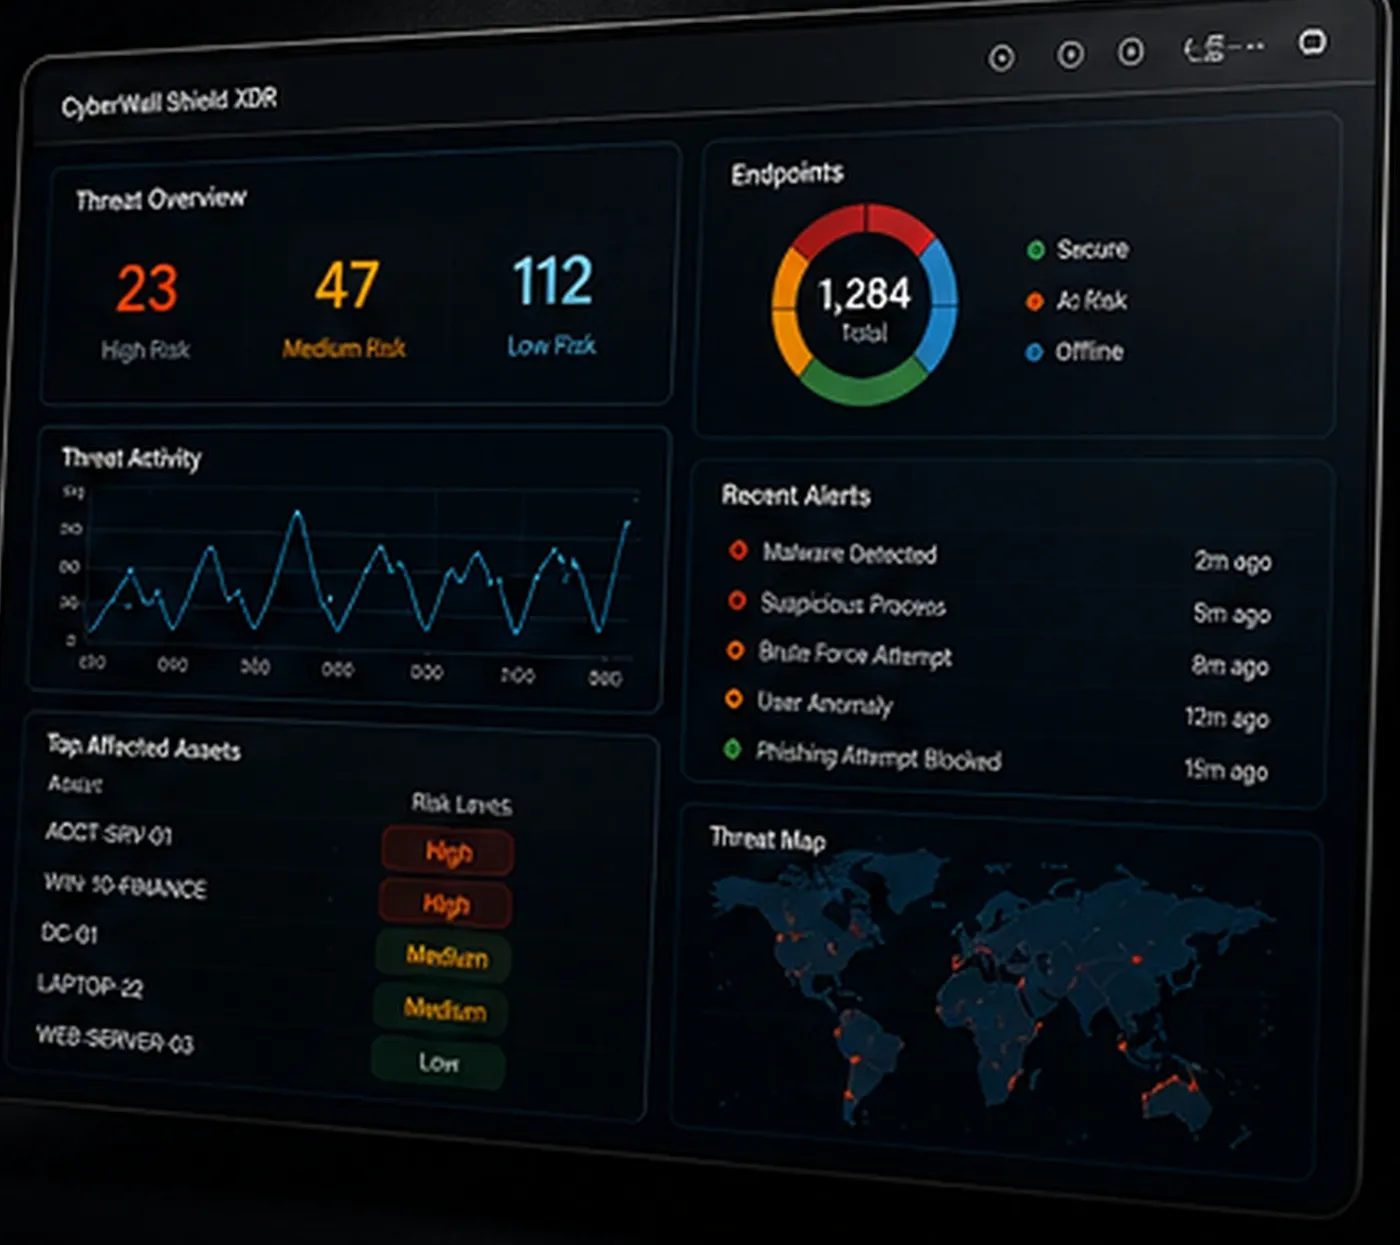
Click around - this is what you see when you sign in to CyberWall Shield. Open alerts, press the buttons, change pages from the menu.
This is the actual product.
Screens from CyberWall Shield as we use it every day. Client names and personal details are blurred. Click a screen to enlarge it.
Check. Fix. Prove.
- 24 automatic checks every day - antivirus, encryption, firewall, updates, screen lock, admin rights, backups, Microsoft 365 MFA and more, saved as dated evidence.
- "Fix issue" on every failing check - Shield shows what will change and on which computers, then fixes it (BitLocker only after the recovery key is saved).
- 16 policies written for you from your own settings; the owner adopts them with a name and title.
- Nothing runs on its own - every fix needs a click and is logged with the person's name.
One set of controls, many frameworks.
One piece of evidence counts for every framework its control maps to.
SOC 2
Trust Services Criteria.
HIPAA
Security Rule safeguards.
PCI DSS
Card payment security.
FTC Safeguards
For financial-service businesses.
ISO 27001
Information security management.
NIST CSF
Cybersecurity Framework.
CIS Controls
Prioritized safeguards.
CMMC / NIST 800-171
Defense contractors.
Readiness, stated plainly.
- A failing check is never hidden - the control stays Action needed until fixed or an approved exception is recorded.
- Missing data never counts as evidence.
- Written procedures count as Partly met until there is proof they are carried out.
- Readiness, not certification. A SOC 2 report comes only from a licensed CPA firm; an ISO certificate from an accredited body.
Common questions
Will this make us SOC 2 compliant?
Shield gets you ready and keeps you ready. A formal SOC 2 report or ISO certificate still comes from an independent auditor, and some records (like signed vendor agreements) come from you.
Who can press Fix issue?
The company owner, plus the people the owner allows. Every fix is logged.
Can a fix break something?
Fixes are chosen to be safe - for example updates install without restarting unless you choose otherwise.